[ 01 ]
Baseline scan
Which laws and standards apply to you, what do your customers ask for and where do you stand today? Within two weeks you have an overview, you know the biggest risks and there is a plan for the next ninety days.
[ interim ciso ]
For software companies and scale-ups that must meet laws, standards and customer requirements. I work out what applies to you, take the lead as interim CISO and make security part of the daily work.
Services
[ 01 ]
Which laws and standards apply to you, what do your customers ask for and where do you stand today? Within two weeks you have an overview, you know the biggest risks and there is a plan for the next ninety days.
[ 02 ]
I temporarily take responsibility for information security and compliance: from risk analysis and policy to customer questionnaires, supplier agreements and reporting to management.
[ 03 ]
From baseline to certificate. I set up the management system, make the controls demonstrable and prepare your team for the external audit.
Need an interim CTO as well, or help with architecture or quality assurance? That is possible too, as an addition or on its own.
Expertise

Dutch Cybersecurity Act (NIS2), Cyber Resilience Act, DORA, GDPR and the AI Act. I translate what the law asks into concrete measures, with the evidence to match.

ISO 27001, NEN 7510, SOC 2 and BIO. A certificate that fits how you really work, so the next audit does not become a new project.

Security questionnaires, supplier assessments, contract requirements and due diligence. One standing set of answers and evidence, so a questionnaire no longer costs you weeks.
Sound familiar?
Approach
One hour, no obligation. Afterwards you know whether I am the right person.
In two weeks I map out which requirements apply and where you stand. You get a ninety-day plan that you can also carry out without me.
I take charge, work with your team and report to management.
I train a permanent successor or your own team and leave everything recorded for the next audit.
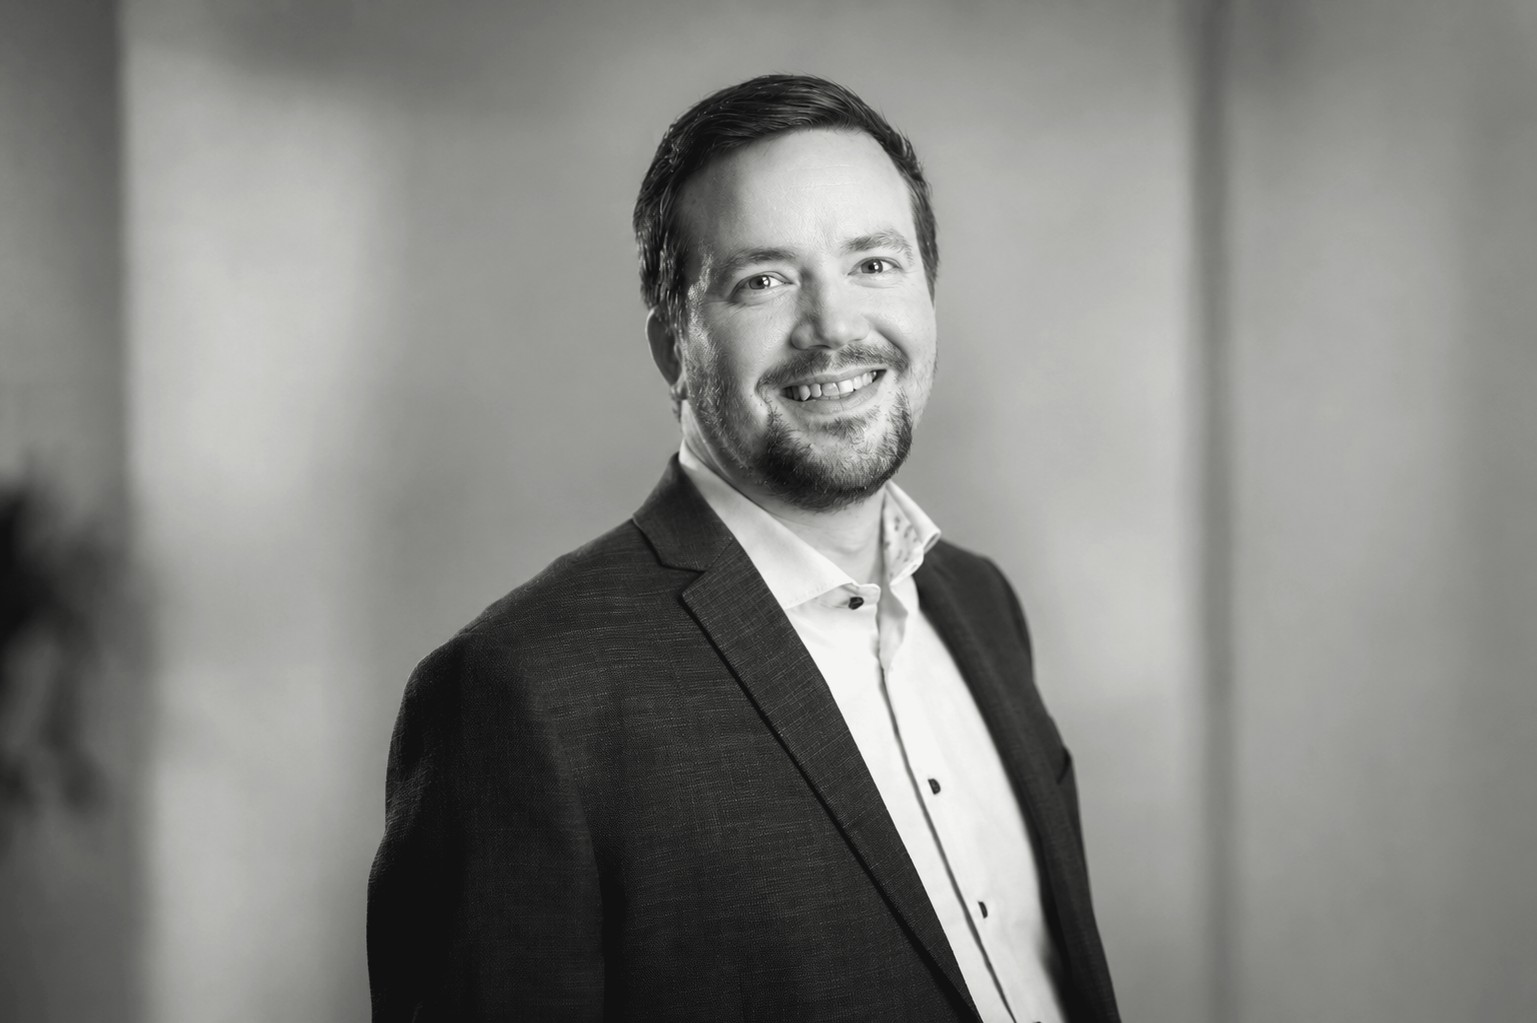
About Erik
I come from software development and have led IT teams for years. That is why I know what a control demands in practice, and can explain it to both management and the auditor.
Tell me briefly where you stand. You will hear from me within one working day.